Tuesday, March 17, 2020

ANOTHER SMB vulnerability? Not for ONTAP!

Well well well.   Imagine that.  Microsoft is announcing another vulnerability in SMB.

For those of you that missed it:
CVE-2020-0796 is a unique ID assigned to a Microsoft-specific vulnerability in their SMB v3.1.1 compression code. https://portal.msrc.microsoft.com/en-US/security-guidance/advisory/CVE-2020-0796

The question always arises: "Is ONTAP vulnerable?" 

Well....  what we do is take the vulnerability and assess it against ONTAP.  We make no assumptions and ensure that ONTAP is either not vulnerable or we log the vulnerability and fix it ASAP.  
Why is ONTAP not automatically vulnerable like Windows?  Doesn't it run SMB?   Well yes it does, but the code that runs ONTAP's SMB stack is proprietary NetApp code. It is a completely NetApp written stack.  ONTAP does not run or share any Microsoft SMB code.  If there are vulnerabilities in the Microsoft code, they are not necessarily in ONTAP code.  
There is, however, a possibility that the vulnerability exists in the protocol standard.  Any time there is a vulnerability in the implementation of a protocol it is possible that NetApp could make the same errors in the protocol implementation leading to a similar vulnerability. 

The bottom line:
For this particular vulnerability, it is in the SMB 3.1.1 compression feature implementation in Windows.  NetApp has determined that ONTAP is not vulnerable to this.  ONTAP does not support the SMB 3.1.1 compression feature and therefore is not vulnerable.

NOTE:   There is no need to post "not vulnerable" responses.  There will not be an official report that says ONTAP is not vulnerable.  


Wednesday, February 19, 2020

NFS and deny permissions

There's always "bonus features" that get stuck into products that may or may not be useful.   But the hard part of all this is when you start using that "bonus feature", then your locked in and... BANG!  They gotcha!  Then when you want to migrate off....   BOOM! You can't. 
Is it really locking you in?  Maybe... maybe not.  There are certain features that are life savers and you need to make a decision on whether or not to really abandon that product and go with another that doesn't have that feature.   For other features, you just need a way to do the same ting in another way.
Once of these features is a "deny permissions" setting on another NAS vendor's system.  This in essence denies anyone from being able to change the permissions of a file via NFS.  This means no chmod's allowed.  Is that a good thing?  Well maybe.  It may allow the permissions to be set initially on a file but all subsequent changes are denied.  This is great, but there's other mechanisms in the world to provide the same or similar behavior.  And why do you really need this?  For one, some unified permissions schemas are so insecure, this is a way to be "secure".
Image result for ignore meme
Deny Permissions on NFS the easy way.  With NTFS.
Lets look at ONTAP and the "deny permissions" flag.   How can you "deny permissions" for chmod in ONTAP?   Well, the easiest way is to create an NTFS volume (or change the security style of an existing volume).   If an NFS client tries to perform "chmod" operations to the files or directories in that volume, the operation will be denied.  This can cause problems with some Linux applications that can't have chmod return errors; like vi.  For this, ONTAP has a setting called "ignore security operations on NTFS volumes" (-ntfs-unix-security-ops ) .  When this is set, ONTAP will return a success to the chmod, which makes the application happy, but in reality, it just discards the chmod op.  This way, the only way to change the permissions is via Windows or SMB.  Now you can use Windows ACLs to further limit permissions and access.  Why is this good?  Well, you can set the initial permissions at the volume level and then be sure that all files and folders inherit the exact same permissions without fail.  If you don't allow SMB access, then noone will be able to change it.

In action?   Why sure.  Here we go.  (Assuming SVMs, CIFS server, protocols, and other Vserver is already done)
1.  Create an NTFS volume
cluster::> volume create -vserver svm0 -volume no_chmods -aggregate aggr1_node1 -size 100G -security-style ntfs -junction-path /no_chmods
2.  Change the setting to ignore the NFS chmods

cluster::*> vserver nfs modify -vserver svm0 -ntfs-unix-security-ops ignore
Then what happens?  Well you need to create the export policy for the volume, but then you just mount the volume and viola.....  there's no way to chmod.  You can't chown either from an NFS client.  You can only change the ACL from an SMB client.
So here I have the volume mounted, touched a file and then chmod'd it.  As you can see, there was no error to the chmod, just a return, but the chmod did nothing.  This is because when ONTAP is presenting an NTFS style volume to NFS clients, NFS security operations cannot  modify the file permissions.  


Bonus Material:   The NTFS permissions can even be locked down beyond what's listed via SLAG (Storage Level Access Guard) in ONTAP.  SLAG allows you to put another set of ACLs on the volume and further deny (SLAG can only limit and not allow more permission) access to the files.

Deny permissions on NFS with NFSv4 ACLs on UNIX style volumes.
You don't want to use NTFS style volumes?  There definitely is another way of limiting access to chmod, and that's via NFSv4 ACLs.  Those ACLs work similarly to NTFS ACLs and can deny rights to change permissions and ownership if necessary.  If you are not familiar with NFSv4 ACLs, go visit my favorite resource for them at die.net (https://linux.die.net/man/5/nfs4_acl).  There's some good resources I've relied on forever.  Here's the catch....  you can't limit the chmod for the file owner.  Bummer.  

How do you do this one?  Let's see.....
1.  Allow NFSv4 on the NFS server and allow the ACLs.  We're assuming you already have an SVM, an export policy and a volume exported.
cluster::> vserver nfs modify -vserver svm0 -v4.0 enabled -v4.0-acl enabled -v4.1 enabled -v4.1-acl enabled
2.  Enable the setting to force the ACL over mode bits to be applied on new files & folders
cluster::*> vserver nfs modify -vserver svm0 -v4-inherited-acl-preserve enabled
3.  Enable the setting to not clobber the ACLs when an actual chmod is run by someone who is allowed
cluster::*> vserver nfs modify -vserver svm01 -v4-acl-preserve enabled
Then you can mount the volume either NFSv3 or NFSv4 and the same ACL is applied to both protocols.  First you do have to set the ACL properly for this to work.  Let's see how this is done.

First set the proper permissions.  What you don't want in there is "write attributes" (capital T), write named attributes (capital N..  and it's optional) and write ACL (capital C)
# nfs4_setacl -a A::testerdlu0002@ntap.local:rwaxtncy testfile
This will allow the user to perform any operation except modify the ACL, owner and mode bits.

So now, when the user tries to chmod the file... viola.. permission denied!


Can you also do it with SLAG and UNIX style volumes??
Well sure you can.  You have to be a little careful with SLAG though.  There are a few caveats.  First, you have to have a CIFS server created on the SVM.  Easy enough.  Second, you MUST have Unix->Windows usermapping working perfectly.  Without it, SLAG won't be applied properly since it used the Windows user creds to apply it.  Third, it also looks to have an implicit default DENY rule at the end of it.  No bueno if you want to ensure the same access.
Here's the policy I was using that had some success.  Notice the 2 deny rules at the top.  The access rights hex value (c0110) translates to WriteEA,Write Attributes, Write DAC and Write Owner in the NTFS permission world.  This basically denies everyone the right to chmod.

cluster::*> file-directory ntfs dacl show -vserver svm0
  (vserver security file-directory ntfs dacl show)

Vserver: svm0
  NTFS Security Descriptor Name: deny_write_attr_everyone

    Account Name     Access   Access             Apply To
                     Type     Rights
    --------------   -------  -------            -----------
    BUILTIN\Users    deny     c0110             this-folder, sub-folders, files
    CREATOR OWNER    deny     c0110             this-folder, sub-folders, files
    BUILTIN\Administrators
                     allow    full-control      this-folder, sub-folders, files
    BUILTIN\Users    allow    full-control      this-folder, sub-folders, files
    CREATOR OWNER    allow    full-control      this-folder, sub-folders, files
    NT AUTHORITY\SYSTEM
                     allow    full-control      this-folder, sub-folders, files
6 entries were displayed.


The bottom line?   Well... to be honest, the only reason that some NAS appliances have this "deny chmod" feature is in order to keep files secure and to enforce a consistent set of permissions across a volume.  Well...  if you really want to do that, let's use NTFS volume security.  That's the easiest.  Then you can manage permissions once when the volume is created (apply inheritable permissions at the volume root) and then its applied everywhere.  If you REALLY Need it in a UNIX style volume.....  You can use NFSv4 ACLs to deny write attributes.  If you ABSOLUTELY need it to apply to the owner too, look into using SLAG.


Thursday, February 6, 2020

Microsoft, ONTAP, and the LDAP Channel Binding Apocalypse

Howdy Folks!  I'm sure that everyone has heard and is panicking about the patch that Microsoft announced around LDAP communication and channel binding.  For those of you that are living under a rock with an early 2000's flip phone, here's the link: https://portal.msrc.microsoft.com/en-us/security-guidance/advisory/ADV190023

Well, let me be your guide around what this means when it comes to ONTAP.  Buckle up, and here we go.
                              

FIRST OFF:  LDAP CHANNEL BINDING TOKENS
The MS update (when it comes out.  as of this writing, it is now pushed to 2H CY2020) will require channel binding tokens(CBT) only if the client supports it.  That is the default registry setting of 1 that the patch will set.  So, when you install the patch and do nothing else, there will be no effect on ONTAP since ONTAP does not support CBT.   At some point, Microsoft may change the default setting to 2, or your AD team or security team may require a setting of 2, but until ONTAP supports CBTs, a setting of 2 is not compatible with ONTAP.   The default setting of 1 or a setting of 0 (never required) is compatible with ONTAP.
NOTE:  ONTAP above includes all releases of Cluster Mode and 7-Mode ONTAP and Data ONTAP.

NEXT:  THE REAL PROBLEM.....   LDAP SIGNING REQUIRED
The MS update will change the behavior of the settings for LDAP signing required.  This means that if you have never touched the setting, it will now behave as if LDAP signing is required in your environment.  Here's a little cheat matrix to help you.


If you explicitly set the LDAP Signing Requirement to "OFF" in your environment, you will have no impact after the patch.  Nothing will change.  The patch will not modify the setting.  Remember though, this will need to have been EXPLICITLY SET TO OFF either in a GPO or registry setting on the DCs.

If you are currently using "Signing required" in your environment (setting of 2), then you have already done everything in your environment necessary to support it.  The patch will not modify, enhance or change that setting.  You will have no impact after the patch.  Remember, you will have had to set this EXPLICITLY in a GPO or registry setting on the DCs.

For everything else, you need to do some changes.


I have an SVM with a CIFS server

If you are already using StartTLS, LDAPS, or signing/sealing for the CIFS security, you do not have to do anything.  Any of those settings will meet the requirements of the patch.  Here's an example SVM with none of the 3 set properly:

If you are like the above and have none of the possible settings set, the easiest setting to modify is the signing & sealing (client session security) option. This is because StartTLS and LDAPS both require certificates and if you don't have a certificate infrastructure in your environment, well...  its complicated.  In order to set signing use the following command:
 vserver cifs security modify -vserver svm0 -session-security-for-ad-ldap sign
Replace "svm0" with your vserver name.  That's it for the CIFS server.

This will only work for ONTAP 9 and higher.  For Data ONTAP 7-mode, the connection automatically upgrades to sign when it encounters an AD where signing is required.  There is nothing additional needed to do for 7-mode.  For ONTAP cluster-mode versions older than 9, you'll need to set up StartTLS.  There's plenty of documentation and resources on how to set up StartTLS for the CIFS server.  I'm not going to go into it here.

I have and SVM with a UNIX LDAP client
Here's where it gets a little complicated due to the amount of permutations of the LDAP config there are.  Now, what I can say is that the same rules apply for UNIX LDAP connections as the CIFS server security settings.  If you are already using StartTLS, LDAPS or signing/sealing for the configuration, then you are in the clear and you are meeting the requirements of the patch.  Here's a screenshot of a client config with none of the 3 set properly"
NOTE:   As of ONTAP 9.5, if you use "636"  for the LDAP Server Port, LDAPS will be used automatically

Now, I am not going to go through all the iterations of possible configurations and what their outcomes are, but I will point you to the best practice and what is the easiest; use the AD-Domain setting, use the bind-as-cifs-server setting, and use the signing & sealing (Client Session Security) option.  Using the AD-Domain setting will automatically discover AD DCs and attach to the closest one using sites and services.  Using the bind-as-cifs-server setting will guarantee a sasl bind and enable the ability to sign or seal.  Then using at least signing for that configuration will use signing for the LDAP connection similar to the CIFS server operation I explained above and satisfy the requirement.

Want to read the official NetApp KB article?  Click on this:  https://kb.netapp.com/app/answers/answer_view/a_id/1103575

**Whew**  Now that we've muddled though alot of the muck on this, I hope you followed me through the configurations and now you know what you need to do to stay operational once the patch hits and gets applied to your DCs.  Apocalypse.....  carry on!


Monday, October 7, 2019

To homedir or not to homedir.....

... that is the question.   Here's the answer:  WHY NOT!

What the heck am I talking about?  Well, its the lesser-used NetApp ONTAP homedir feature.  What the heck does it do?   Make home directory provisioning, configuration and management so much simpler!

So, that's a pretty bold blanket statement, but the benefits of using the homedir feature in ONTAP is just so overwhelming, there's really no downside (besides the initial configuration and user provisioning process modification) to enabling and using it.  In essence, it's really a best practice when using ONTAP for home directory serving.

What is this homedir function you talk about?   Well it's a feature in ONTAP that created shares and exports on the fly based on the client's usernames that are presented to ONTAP during the mount or drive map process.  This makes it so much easier to provision users, home directories, permissions, quotas, and everything in between. Take the guess work out of it all!

Does it help?
Yes!  There is actually a recent Microsoft Windows bug rolling around in build 1803 that can cause some performance issues.  When you use that pesky little search bar in Windows Explorer and search a mapped drive, and that mapped drive is actually a folder within an actual share, then Windows does some real deep searching all the way back to the root of the share.   WHAAA???  There are other stupid things happening with the Windows clients too that can cause some weird performance issues when there is a lot of file enumeration going on.  Most of this client behavior is happening on the home drive, or even worse, a roaming profile drive.  This is because when you create a home directory share, you create a single folder, share that folder, create everyone's home directory off that folder, then have the users map the folder level.  (something like mapping H: to  \\server\homedirfolder\username).  No I'm not going to get into the minutia of the behavior since MS has done some work to fix it, but it's there nonetheless. Let's all use this awesome ONTAP feature to mitigate these issues.

Do I really need to know how it works?
Maybe.   It's actually not that complicated.  When a user connects to the "homedir", ONTAP just looks into a few volumes specified for that user's name on a directory and then creates a hidden share on the fly and lets the user attach to it.  That's it.  It's that simple.  Nothing more, nothing less.

Why do I want it?
There's a few things that make this so much more simple than the traditional way of creating a "homedir" share and mapping sub-directories to it.

First of all, it's simpler to expand.  What if the volume serving your homedir is full?  What if it needs more performance?  What if we need to create more volumes?  Split it up?  You can see the problems there.  Let me give you a quick demo.

ONTAP System Manager is showing me that I only have 4 homedir volumes in the searchpath.  I want to add another.  Let's say we're bringing on more staff.

Let's just add the volume to the search path....
And voila!!!  It's there!


That was easy!   As long as all the homedir volumes are in the same SVM, then you can add as many volumes as you want to the search path.

Why else do I want this?  Well, the only thing you have to do when provisioning a new user is to create the user's homedir folder in one of the volumes of the search path.  No need to create a new share... no need to create a new volume.... no need to do anything else except create the folder and apply the permissions!  You can even automate this with PowerShell!  You can even balance the amount of homedirs in each volume with the PowerShell script!!!!

I'm Sold!  How do I implement this?
It's easy.  Just create the homedir share and add volumes to the search path.  With System manager... its an all-in-one process!!!
Create the home directory share.

Here's where you can get creative.
For the name, this is what you will be putting into AD for the home dir path.  There is a caveat though.   If you create a non-unique name and have more than 1 user log into a machine at the same time, then there can be issues.  Why?  MUP cache.  What???   Yes. I said MUP cache.  What in the blazes is that?  Well, when the client mounts the home directory (let's just call it \\svm\cifshomedir), what is going on under the covers is some DFS magic to actually point it in the right direction.  The clients cache this DFS magic.  Unfortunately, that caching happens at the machine level.  So when user jimbobbillyjo logs into the Windows machine and has their homedrive connected, then the client machine's DFS cache says that \\svm\cifshomedir is actually \\svm\jimbobbillyjo$.   Now when user georgemcf logs into the same machine (like with a user switch) then when it tries to map \\svm\cifshomedir, then it's actually trying to mount \\svm\jimbobbillyjo$.  That won't work for poor georgemcf.
In order to just bypass all that nonsense, use the appropriate abbreviation in the name.  %w will be the most common, then you can use %username% in the drive mapping in AD.

So what do I need for AD?
Just set up the homedir.  There are several schools of thought.  
* Home Folder:  This is the most obvious.  ADUC gives you a drive letter and path.  This will also give you some variables once logged in like %HOMEDRIVE%, %HOMEPATH% and %HOMESHARE% that you can use to do more with.
   For automation, you can use variables.  I would use \\svm-name\%username%.   Then ADUC will translate that to username.


* Roaming Profile:  Its the exact same as the Home Folder above, but its called the Profile path in ADUC. 

* GPO for mapped drives:  This is more of a fan favorite. No need to set something for every computer account.  If this is a domain-wide GPO, then everyone gets the drive mapped.  This is where you need to use the variables though.
  The downside?  You don't get any of the cute variables.


Tuesday, August 13, 2019

FlexCache now FREE!

Recently NetApp reintroduced FlexCache into ONTAP where both the origin and the cache can run on ONTAP 9.5 or higher.  That did come with a license; term & capacity based.  Well, the great folks at NetApp have decided that it should be part of the ONTAP package.  That means that its now freeeeeeeeeeee. 

Hold your horses.  That doesn't mean that you can now go creating FlexCache volumes all over the place in ONTAP.  There's no magic that can do that.  That just means you still need to get a license, but it costs $0.00!  Go bug your NetApp account team to go get you one.  I
n a future ONTAP version, you will be able to create FlexCache volumes without a license.  This may even be a P release!  (All the more reason to upgrade to P releases)

You want to kick the tires?  Go on over to https://www.netapp.com/us/info/what-is-flex-cache.aspx and see what you can do.

Thursday, April 11, 2019

LDAPS is dead! Long live LDAPS!

So, as a TME for NFS, Name Services and SMB, I always get the question...

Does ONTAP support LDAPs??

StartTLS is insecure compared to LDAPS, right?

Well, let me tell you something........


LDAPS is sooo 90's.  There!  I said it!  90's?  really?   Yep!   RFC1777 was published in 1995!  And guess what?  There was no standard written for LDAP over SSL!  This was just assumed and taken from HTTPS at the time. The LDAP vendors took it, and rolled with it.

Enter LDAPv3.

RFC2251 was started and completed in 1997.  That didn't have any additional verbiage for on-the-wire encryption, but when RFC2830 was written in 2000, it made an extension for LDAPv3 specifically for StartTLS.  RFC4511 combined them into one LDAP v3 standard in 2006.  Once LDAP v3 was ratified and made it into mainstream in the early 2000's, LDAP vendors started to deprecate the LDAPS encryption method for StartTLS.

Deprecate.   That's a big word.   But what that means is that to "be usable but regarded as obsolete and best avoided, typically due to having been superseded."  Don't believe me?   Check it out:
https://www.openldap.org/faq/data/cache/605.html
https://directory.apache.org/api/user-guide/5.1-ldaps.html
https://en.wikipedia.org/wiki/Lightweight_Directory_Access_Protocol#Protocol_overview
I can go on....  Just do a Google search for LDAPS deprecated and see.

Clustered Data ONTAP started without any LDAPS support in favor of StartTLS because of the above reasons.  All LDAP vendors had to support the StartTLS extension because it was part of the standard.  Also, because LDAPS was deprecated, it could be yanked at any time.

But....  StartTLS is not as secure as LDAPS!!  It runs over a plaintext port!

Well, if you leave your LDAP install wide open, sure.  Your LDAP is still insecure.  But there are countermeasures that you can deploy to make sure StartTLS is secure.
  1.  Make sure that StartTLS is enabled.  DUH.
    This requires certificates.   Certificates are hard, but learn them.  They make things secure.  For internal, self-signed certs are OK as long as the domains and permutations of them are accounted for.
  2. Prevent queries without StartTLS.
    Now that StartTLS is enabled, you can set up LDAP servers to prevent LDAP commands unless the connection is StartTLS upgraded.  This can be done on a DIT (directory information tree) basis. 
  3. Prevent LDAP binds without StartTLS
    There is also a way to prevent BINDs from happening in plaintext.  Consult your LDAP vendor's documentation on how to do this.
  4. Prevent LDAP clients to send plaintext creds
    You still want to prevent your clients from sending their credentials in plaintext.  This means setting the minimum bind level at SASL.  The credentials passed will also be encrypted.
Doing all this will ensure that the LDAP communication is always secure.

How do you configure LDAP to work with StartTLS in ONTAP?  Easy.  Install the root certificate for the LDAP server's enterprise and then change the LDAP client config for -use-start-tls true and you are set to go.
Here's how your traffic looks: 
I don't see any holes in there.  Application data means its encrypted and is all buttoned up!  

What about ONTAP and LDAPS?   Well...  low and behold......   9.5 introduced the ability to do LDAPS.   Even though its deprecated and there are alternatives, the ability to do LDAPS was granted.
How do we do it?
Change the port in the ldap config to port 636.  Make sure -use-start-tls is turned to false and the same enterprise root cert is installed into ONTAP.  Is this more secure? Less secure?  Who knows.  Not my debate.
Here's what your traffic looks like:

You decide.  They look almost identical to me except for the LDAP START_TLS packets at the beginning.

Wednesday, December 19, 2018

FlexCache is BAAAAAAACK!!!!

We're starting to hear alot of "Global Namespace" in the industry.  Buzz, buzz, buzz.  Well, what really is a "Global Namespace"?   Well, it can be broken into 2 categories.

  1. Your whole data structure is under one "root" volume and the data is actually stored all over the place.  But it's all under one directory tree with soft links, symlinks, junction points, widelinks, and a whole bevy of tricks.

    OR
  2. Your dataset is available in multiple places in a read-write configuration (caching) and no matter where you are in the company's network (via VPN, overseas, in a remote office, at the datacenter) you get a similar response time to that dataset and its all read-writable.

Which one do YOU want?

The first one SOUNDS great, but what benefit does it have?   Well, now you don't have to go search the P: drive AND the M: drive AND the T: drive for what you want, you just have one MASSIVE-looking drive.  But your still searching through the subdirs to find your data.  It's nice... but just smoke and mirrors and your gaining VERY little.

On the Linux side, its a LITTLE better since your automounter just mounts stuff automagically under some path (maybe /data) and everything underneath looks like a single file system.  BUT you have the same Windows dilemma.  Is it REALLY better for your clients?  Also think of applications that now have to go down some unGAWDly path to get at its data.

THEN you have the whole performance issue.  Your Windows P: drive, which is the same as the Linux /data/pdrive path is hella ethernet miles away and performance SUUUX.  

Sooooooooo

Let's look at the second one.  Now this sounds good, but is it?  Well, this means that your data is in multiple places at once and that when you look at it from anywhere in the world, the performance is "local" and its a writable copy.   Awesome!  How does all this coordinate?  Well, ONTAP has a cool new thing called FlexCache.  Well, is it really new?   Well, yes it is. But it isn't.  
We had something in 7-mode called FlexCache.  It was good for its purpose, but lacked enhancements.    Bring the data in a read-heavy, but still writable capacity closer to whatever needs it. It was great for what it did, but the potential to move it forward and give it more features was limited by the backend technology.  Enter FlexCache in ONTAP starting with 9.5.  Its a whole new rewrite of the technology which can give so much more!

First of all, what are the use cases?  There are a few.  The first ones that come to mind is working on the same data in multiple places.  This is an example of AI, EDA, Media Rendering, Code distribution, and other similar workloads.  You have a single "master" data set, but you want other pieces to be able to read the same data and write some results or something into that same dataset.  The next one that comes to mind is creating multiple read-heavy copies to keep the "hot volume" syndrome down.  We all know there's challenges when multiple clients are reading the exact same file(s).  So let's spread the load!

So...  how do I get it and use it?
Starting in ONTAP 9.5, the new FlexCache is available. Give it a spin.  Let your mind explore the options you can use this new feature for.

I do have a Technical Report for the deep dive.  You can find it here:  https://www.netapp.com/us/media/tr-4743.pdf

Go for it!


Thursday, June 1, 2017

Does ONTAP need SMB1? No!

There are some rumors flying around that ONTAP, the OS behind NetApp storage appliances require SMB1 to operate in a Windows AD environment.  Well???


That would be false.

Data ONTAP 7-mode has had SMB2 available to it since SMB 2.0 was introduced.   When the OS talks with Domain Controllers for authentication, SMB1 was recommended for the longest time, but several years ago, that recommendation was lifted due to some enhancements in the SMB2 protocol.

Clustered ONTAP has had SMB2 available since inception and has had support for SMB3 since it's inception.  At some point, there still was a dependency on SMB1 for Domain Controller authentication traffic and some other features, but that has since been eliminated.  Those version are 8.3.2P5, 9.0P1 and 9.1 and above.

Starting in ONTAP 9.2, you can actually turn off SMB1 completely with the following 2 commands:

vserver cifs security modify -vserver svm1 -smb1-enabled-for-dc-connections false

vserver cifs options modify -vserver svm1 -smb1-enabled false

DONE!
Image result for drop the mic done


Wednesday, March 22, 2017

SMB1 is baaaaaad!

Every once in a while, something comes along in the IT world where everyone panics.  And I mean PANICS!  The lastest SMB1 vulnerability is that panic generator.  It's so bad that they created 6 different CVEs to cover it.
Vulnerability title CVE number
Windows SMB Remote Code Execution Vulnerability CVE-2017-0143
Windows SMB Remote Code Execution Vulnerability CVE-2017-0144
Windows SMB Remote Code Execution Vulnerability CVE-2017-0145
Windows SMB Remote Code Execution Vulnerability CVE-2017-0146
Windows SMB Remote Code Execution Vulnerability CVE-2017-0148
Supposedly this zero-day vulnerability can leak information and allow for remote code execution.

What?   Zero day??   Remote code execution? Huh?  Let me try to break this down for you and give you the "what this means to me" speech.


1.  Zero-day Exploit

This is just a highly technical term to say this vulnerability has been in place since the initial release of this code/function/feature.  For this SMB1 vulnerability, this means that the vulnerability has been in Windows since at least Windows Vista (which is the earliest version that Microsoft still supports), and could possibly even be in Windows XP, Windows 2003 and Windows 2000.  But since Microsoft no longer officially supports those Windows versions so they won't divulge that information.

2. Remote code execution

This one is a little more nebulous of a term.   Well... ok you can execute something remotely on some machine.   Great!   I can do a "dir" on a remote machine.  Which machine?  The "server" or the "client"?  With SMB1 there is the concept if the "server"; the machine serving the files.  and the "client"; the machine that connects to the "server" to read, change or delete those files.  These particular SMB1 vulnerabilities allow for a malicious (read: highly modified) client to exploit that vulnerability to run commands on the SMB server. This can lead to being able to download things like password databases and other mean things.

TURN OFF SMB1!

The SMB1 code is old.  Ancient in fact.  It was developed for Windows 2000.  It's inefficient, clunky and chatty.  That being said, there are still devices out there that use it and cannot use anything newer.  Network printers, Linux hosts (fairly recent ones too) and a number of embedded systems still use the old SMB1 code to communicate and cannot use the SMB2 or 3 protocol to communicate so turning off SMB1 completely in your environment may not be possible.  What you can do in this situation is to turn off the protocol on devices that do not require any SMB1 connections to it.  Microsoft has a way to do this through GPOs (Group Policy Objects).  There is a good Technet blog on this here: https://blogs.technet.microsoft.com/filecab/2016/09/16/stop-using-smb1/

But I have a NetApp filer and can't turn off SMB1.   What can I do?

NetApp, both 7-mode and clustered Data ONTAP have SMB servers built in.  If you have them licensed, then you can serve Windows file shares through it.  Is it vulnerable?  Probably not.  The vulnerabilities with Windows, and specifically with these SMB1 ones are within the Windows Operating System code.  Data ONTAP does not run Windows Operating System code.  It has a custom built SMB server that adheres to the protocol standards, but the source code that runs that protocol is completely different than the Windows source code so the risk of having the vulnerability in two completely different implementations are almost non-existent.


How do I know if I still need SMB1??????

With devices still around that require SMB1 for their functionality to work, You need to be informed if devices are still using it.  The way the SMB dialects work, the negatiation on which version to use is basically a highest common denominator type negotiation.  When the client connects to the SMB server, the client sends all the SMB dialects it supports.  (SMB1, SMB2, SMB2,1, SMB3, etc)   THe server then picks the highest common version.  So if a server supports SMB1, SMB2 and SMB2.1 and the client supports SMB1, SMB2, SMB2.1 and SMB3, the result of that negotiation will result in an SMB2.1 conversation.

In 7-mode, you can see which version clients have been negotiated to by running the command:

cifs sessions -p smb

Then you get the output as follows:

Server Registers as 'TOASTER' in Windows domain 'MYDOMAIN'
Root volume language is not set. Use vol lang.
Selected domain controller \\TOASTER for authentication
====================================================
PC IP(PC Name) (user) #shares #files
10.10.1.15() (MYDOMAIN\administrator - pcuser) 2 0


The above indicates that you still have a device at 10.10.1.15 running SMB1.

In cDOT, you have a similar command:

cluster::> cifs session show -protocol-version SMB1

which outputs


Node:    cluster-01
Vserver: CIFS-SVM
Connection Session                                        Open            Idle
ID         ID      Workstation      Windows User         Files            Time
---------- ------- ---------------- ---------------- --------- ---------------
4268056359 1       10.10.1.15      MYDOMAIN\                0              5s
                                    administrator


and you can tell which systems have negotiated to SMB1.

Can I firewall it?

Well....   yes....    well..... no.....   well.........

There is but one TCP port that all SMB dialects use and that is port 445.  If you block port 445 within your internal network, then absolutely no Windows File Services will be available regardless of SMB dialect.  BUT I fully suggest that at your internet connection, you block all inbound and outbound connections to port 445!  It's always smart to allow only absolutely necessary traffic in and out of your network but that's getting into a post for another time.

Thursday, March 3, 2011

Facebook https browsing can be turned off by applications.

For those of you playing along at home, we recently learned that Facebook has turned on secure browsing on it's whole site.  You can accomplish this by checking the "Browse Facebook on a secure connection (https) whenever possible" box in the Account Security section of your Account settings.  Now we know that this stops local hackers from stealing information when you are connected to a the network and this prevents advanced hackers from engineering hacks that can dump your information to them.  But I found something interesting the other day while auditing my applications settings.


This is not working so well.


As I went through some of my applications, I wanted to refresh my memory of why I installed some applications.  I click on the application's page in Facebook and I get a page that tells me that I need to switch back to http (non-secure) browsing in order for the application to work.  


So I play along.

Now to check the damage.   I look at the checkbox that I know I have checked previously to browse in https and it is not checked anymore!  WOW!  Facebook doesn't even let you know that this is a PERMANENT CHANGE TO YOUR ACCOUNT SETTINGS!!!!!


Just all the more reason to do what I do. 


Audit your applications!
Go through your list of applications every once in a while to make sure that nothing has crept in there that you don't want.  If that has happened, immediately remove the app from your profile.
Audit your settings!
The same should apply for your settings.  Go through your settings every so often to ensure that what you have set in the past is still applied.

As always, remember that in the end no one is responsible for your information but yourself.  Always check and double check to make sure your information is as private as you want it to be.

Monday, February 28, 2011

Facebook security http vs. https questions answered

There's been a lot of talk on Facebook lately about http and https and how to change it. Do any of the folks touting this wobegone actually understand what is going on here?  Do YOU know what the difference between http and https is?  Let me try to explain.

When a web browser tries to get to a web site, there is a conversation that happens in the network between the browser and the web server.  Basically you browser gives the web server a bunch of information about itself and then asks the web server to transmit back the page it's requesting.  When you're browser address bar has http:// in front of the web server, this happens in "plain text".  This means that anyone that can see the network traffic between your web browser and the web server can read in plain words what is going on in that conversation.  When you are writing an email, writing a Facebook status update, filling in a form on a website, writing a Facebook message, or sending ANY data to a web site, anyone can read that data that really wants to.  Now, this can happen only at the time that you hit save, send, login, update, or any other button that uploads the information.  As soon as the information is uploaded, that's it.  Noone else, besides the folks you sent it to, can read that data.

Now, when you're browser address bar has an https:// in front of the web server name, then the conversation is a little more involved.  First your browser asks the server for it's "keys", server certificate and then goes out to a certificate authority (such as Verisign, Microsoft, or others) and makes sure the server is who you think it is.  Then your browser takes the "keys", looks at it's own "key" and creates an encryption "key" that will scramble the data that is sent back and forth.  The server then looks at that key and makes sure everything is OK.  Then all data back and forth from the server to the browser is sent coded with the "key".  If someone were to look at that conversation in the network, it would look like gobbledygook to them.
This is the preferred way to log into web sites (since you don't want to send your password over the network so that anyone can read it), send emails, Facebook messages, web site forms, etc, etc, etc so that no one can read the information you are transmitting.

Why is everyone worried about this right now?  Because of Facebook "hacking"?  Will this prevent this???

NO!!!

There are very few opportunities to do this type of hacking. The first is an open WiFi network.  Open means that you have to do nothing to connect to it besides hit the button on your computer or phone that says "Connect".  If you did that, and I did the same thing, I can run a program in the network and listen to everything your computer/phone is saying out on the internet.  If you connect to a WiFi that is password protected, then I can't listen in because the WiFi network does basically the same as the web server in the https:// scenario.

The other two opportunities I have to do this is to send you a bogus email with a link to Facebook that looks like Facebook, but really is my bogus server where you put your information in.  Then my server records that information and sends you on to Facebook so you don't suspect anything.  The last one is that I need to hack into the internet.  This is a little more difficult since I will need to get into network devices owned by AT&T, MCI, Sprint, etc.  Not that easy.

Although this is always good practice to make sure that whenever you are sending private information to a web server, that you ensure https:// is in the address bar, this is not how many of the email and Facebook scams are getting your passwords.  They are getting it by "brute force".  Basically, they are just trying a bunch of passwords and getting a success because yours is easy to guess.  (and don't think you're being clever by using P@55w0rd).

Thursday, February 18, 2010

Over 75,000 systems compromised in cyberattack

Over 75,000 systems compromised in cyberattack
via computerworld.com

Security researchers at Herndon, Va.-based NetWitness Corp. have unearthed a massive botnet affecting at least 75,000 computers at 2,500 companies and government agencies worldwide.
The Kneber botnet, named for the username linking the affected machines worldwide, has been used to gather login credentials to online financial systems, social networking sites and e-mail systems for the past 18 months, according to NetWitness.
A 75GB cache of stolen data discovered by NetWitness included 68,000 corporate login credentials, login data for user accounts at Facebook, Yahoo and Hotmail, 2,000 SSL certificate files and a large amount of highly detailed "dossier-level" identity information. In addition, systems compromised by the botnet also give attackers remote access inside the compromised network, the company said.

 Read entire article

Posted using ShareThis

Saturday, February 13, 2010

Passwords make a difference in keeping your accounts safe from hackers

Lately I've had an influx of people that have had their Facebook, Gmail, Yahoo and other accounts hacked only for someone in Nigeria to ask me to wire them money.  Do they really think that I am going to wire $2000 to someone I have just reconnected with?  No.  What I usually do is throw in a stumper in the chat.  Something the hacker won't have a clue about.  Not something that is true, but something that is false because the hacker will agree.  The other day someone asked me to wire them $3500 to London.  Now I haven't seen or heard from this guy since 8th grade so the fact that he's asking for money is already throwing up red flags, but I go with it.  Then I ask "How's my best UVA roommate doing?"  He answers; "I could really use the help."  Now, I know he went to Virginia Tech and saying he went to UVA would be like branding him with red hot pokers.  Furthermore, we did not even go to school together so being roommates was definitely not the truth.  At that point I knew his account was hacked.


How did his account get hacked?  Every account you open up on the internet requires a password.  It's the old daunting "what password can I make up today" scenario.  Most of us have one password that we use over, and over, and over, and over, well.... you get the point.  How secure is that password?  Can I guess it? Is it a variation of your username, real name, wife/girfriend's name, kids' name, dog's name?  I can guess those.  Most of the time, the hackers run programs that just try a bunch of passwords in a list.  This is what I call the "well known passwords and variations" list.  Do you really think that Pa55w0rd is a unique password you thought up and was cool?  No.  As soon as they get one password, they look for other accounts.  They then try the same password on the other accounts.  Once they have your email account, watch out, because they can reset passwords on just about any other account on the internet you created with that email address.


So, you ask, what is the casual, non-geeky internet user to do?  


Build a better password.  There are plenty of random password generators out there so use one.  When you register for a site, make sure that the password is random.  Now, you ask, how do I keep track of all these passwords?  I don't want to have to remember a different gobbledygook password for each site.  Well here's where technology comes into play.  In your browser, you have the option to save the password for each site.  Use that.  Many security experts say not to use it, but I say go for it.  There are only two scenarios where this poses a risk and those are when your computer gets physically stolen or totally hacked into.  I'll put up another blog post about securing your computer so that nothing can get accessed when it gets stolen, and someone trying to hack into YOUR computer doesn't really happen much anymore.  You can secure your computer against that with good anti-virus, anti-spyware/malware and a decent firewall.
If that doesn't tickle your fancy, you can use a password manager.  This is a program that you install on your computer that keeps track of all your passwords for the different sites.  Some can even automatically log you in or copy & paste your password onto the webpage.  My personal favorite is KeePass password Safe. (http://keepass.info)  This password manager will not only keep your passwords, but will automatically generate a new random password for you every time you create a new site.  The second bonus, it's FREE.


Give better answers.  Many of the sites ask you some "challenge questions".  "What's your mother's maiden name?" or "What city were you born in?" are the most common.  These are also easily guessed.  I can research the 'net and find out where you were born or what your mother's maiden name is without even having access to anything but your full name.  Here is what I like to do.  Make up your own and rotate the answers.  Put together a decoder key of sorts.  Every time a site asks for your mother's maiden name, put in your birthplace, or your first pet's name, or the street you grew up on, or even better some non-sensical answer. Just make sure you have a good decoder sheet for it.  You can also use the KeePass Password Safe to manage this since each site has a "notes" section.  In here you can put in the challenge question and how you answered it.


Stay safe out there on the 'net.  It's powerful, fun, entertaining, and dangerous.  When you put a lock on your house, you use a unique key that's hard to guess what the ridges look like.  You don't use one that has no ridges or only one.  Do the same for your online "house".  Use a good key to lock it all up.

Thursday, January 14, 2010

Google Turns on Gmail Encryption to Protect Wi-Fi Users

via Wired.com

Google is now encrypting all Gmail traffic from its servers to its users in a bid to foil sniffers who sit in cafes, eavesdropping in on traffic passing by, the company announced Wednesday.
The change comes just a day after the company announced it might pull its offices from China after discovering concerted attempts to break into Gmail accounts of human rights activists. The switch to always-on HTTPS adds more security, but does not help prevent the kind of attacks Google announced Tuesday.
All Gmail users will now default to using HTTPS, the secure, encrypted method for communicating with a remote server, for their entire e-mail sessions, not just for log-in. Session-long HTTPS has been an official option for Gmail users since 2008 (and unofficial for much longer), but Google says it hesitated turning it on for all since the encryption does slow down the service.
“Over the last few months, we’ve been researching the security/latency tradeoff and decided that turning https on for everyone was the right thing to do,” Gmail Engineering Director Sam Schillace wrote in the Gmail blog.
This option often wasn’t necessary when people used fixed and trusted connections, such as their home or office DSL or cable lines. But as Wi-Fi connections, especially public ones, became more popular, hackers began using simple sniffing software to snoop on people’s online activities with the goal of stealing passwords.
Still, the switch doesn’t encrypt  e-mail — it simply encrypts the communications in transit between Google’s servers and a user’s computer — the same as when you use your bank’s website. E-mails sent to other people are transmitted in the clear as they have always been. True encrypted e-mail can only be read by the sender and receiver, regardless of how they move across the internet.
For those whose schools or workplaces that routinely monitor employee or student internet usage, the change also shields their e-mails from the IT department.
A coalition of privacy and security experts called on Google publicly to make the change last June, saying that Google was putting millions of people at risk by not using encryption as the default for their so-called cloud computing services.
Users who find the service slows them down or determine that it’s overkill for their needs can turn the HTTPS off in their account settings.
Rival free e-mail from Yahoo and Microsoft do not use HTTPS throughout their sessions, nor do social networking sites or other so-called cloud-computing services.
Instead, most of those services use the secure “HTTPS” protocol only for logging in, and fall back to unencrypted browsing thereafter.Failing to use HTTPS full time increases one’s vulnerability to a host of nasty hack attacks when using an open or badly secured network, particularly a public Wi-Fi spot.

Posted using ShareThis

Tuesday, January 12, 2010

Another new year and a new focus

So I've had 1 post in the last year. That really pathetic. After looking at the last year or two in happenings and other things, I will post some hints and tips on personal technology and security. There's been a few friends that have had their Yahoo, Facebook, GMail, and other online accounts hacked.  The worst thing is that the hacker is exploiting the relationship that person has with their friends/followers/contacts to extort money or other things.  Lets see how this goes.

Thursday, July 9, 2009

Lost in mobileland

I think that I've given up on my Palm Treo 680. It's lived a good life, but it has failed me. I put it in the beach bag the other day at the pool so as not to get it wet. But according to Murphy, it'll get wet somehow and it did. Nothing too awful, just looked like a few well placed drips onto the case. The battery was dead at the time so I went to charge it. After a while I came back to it to check it out.... it was trying to sync. Hmmm..... so let's throw the cable on it and let it sync. OK. Now take the cable off, and it tries to sync again. Not good. After a few rounds of this, I've determined the phone is shorted out on syncing, hence unusable. So I throw my SIM card into an old Moto Razr of my wife's. Alright. I have a phone.
After a few minutes, I understand how awful this really is. I go to text a buddy of mine... and my address book is still on my palm and sync'd with Google, but not on this phone. Can I get my address book on there? Probably not. So I just look up his number on Google and then text him.
Then one of my twitter friends tweets something interesting with a web link. Alright, this this has a web browser. I go to the link and get a 413 error. (basically, this means the web site isn't compatible with a dinky Razr web browser). Darnit! Strike 2.
Then I get this text. "Wanna have a few beers?" Great. Sure! Uh Oh... who's phone number is this? Back to Google. Oh. Ok. It's one of my other buddies. Sure.
Then I want to tweet something. I've done it through text before, no big deal and plus, Twitter updates my Facebook status automatically. So I tweet......... About an hour later, not literally, but not too far off, I have tweeted two sentences! Wow. This is really starting to bother me.
The bottom line is that I have been pretty spoiled about having a smartphone with a full QWERTY keyboard. I can't live without another one. I can't surf, text, tweet, facebook, play games, use apps, take video, or store alot of things on this darn phone. I don't even have 60 texts in it and it says the memory is almost full. Boo. I'm definitely spoiled.

Tuesday, December 30, 2008

Looking at the New Year


Wow. I really can't organize myself to have at least a post a week? I would really love that. I guess I have my answer to the question "What will my new year's resolution be?" I get so consumed in work and home that my other endeavors suffer. Well, no more. I am going to give myself a boot in the a$$ and put the nose to the grindstone when it comes to other endeavors. I will be trying to document my steps here on my blog so stay tuned.
I'm still using most of my stuff on Google. Google Notepad and Google Documents have been valuable resources. I've been using Google Documents to create notebooks about stuff. One notebook has ideas, tasks and other things about my garage. Another has stuff about trying to make a Linux home computer and what packages to put on it. Yet another is a few recipes that I clip off the internet. My wife and I love trying new things at dinner.
Google notebook is something I use more for web-clipping than anything else. I also track changes that I make in the presentation of this blog. I know there's a little convergence in the two programs right now, but that'll get ironed out later.
I still have not found a good tasks program for Google. Now they just did implement Google Tasks in GMail. You can read about it here. I have not yet used that feature. I have been using Remember the Milk with a little bit of success, but I'm not fully sold. I cannot sync it with my Palm Treo 680 and would really love to have that feature.
And awa-a-ay we go!

Monday, November 10, 2008

Halloween

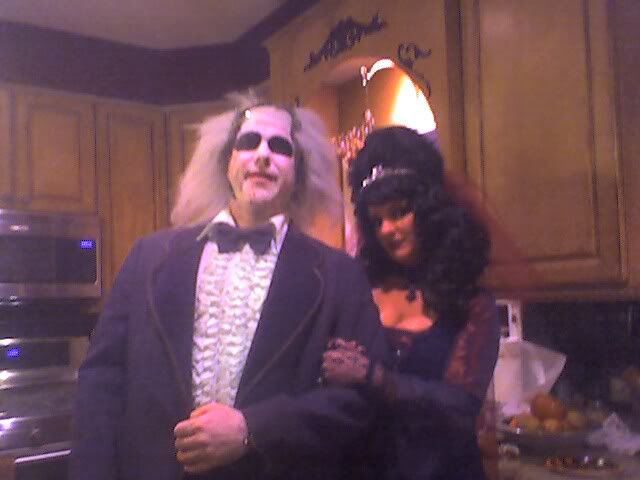
It's a little late for Halloween, but what the heck. I end up rockin' it like Rosie Greer for the month before halloween. I make as much as I can for all the family costumes. We're not the "buy it off the shelf and wear it" type of people. We scavenge, sew, create, improvise and just about do anything to get that look we want. This year, the wife and I went as Beetlejuice and Lydia (the wedding scene).
I was pretty intimidated by the makeup part, but I think that I scooted by. I used a relatively cheap Beetlejuice wig/cap and enhanced it a bit with real moss from a craft store and some white face makeup. I found the vintage 70's tux complete with ruffled shirt at a local antique/vintage store. That was one awesome find. As for the wife, the dress part is bought, but I made the veil/train with some tuile from the local fabric store and the sewing machine. The tiera is from HS when she was homecoming queen. The choker is from an older costume.
The kids weren't that hard or elaborate. My son was ObiWan Kenobi and my daughter was Willy Wonka. For my son, I sewed together a top from a few patterns online. (There's a plethera of Star Wars geeks online that well tell you how to sew a "proper" Jedi costume) We then get a "monk's robe", cut it up a little, a pair of sweats and some boots and viola. My daughter was even easier. At the goodwill store, we found a black button down shirt, a maroon/purplish trenchcoat and a pair of old black penny loafers. The I picked up a brunette "supermodel" bob wig and I had an old top hat from an old costume. There. Willy Wonka!

Wednesday, September 24, 2008

Work - Life balance in a connected world

A friend of mine posts a blog entry the other day about work-life balance and it got me thinking. These days, competition is fierce, the Fortune 500 companies are locking down their employees as if they own them. State and Federal governments are even worse! This really breeds a workforce that is pretty separated from their employer. We are pretty much locked into a 9 to 5 world when we are living in a 24-7 world. Not the best for morale, productivity, efficiency, effectiveness, and motivation.
With me being a geek's geek, I have the answer. A 24-7 job. Now stay with me here, this is where it gets complicated. We all have the tools to go mobile; laptops, iPhones, Blackberrys, Windows Mobile smartphones. Some of us even have other tools that are pretty cool; cellular "network" cards for the laptops, cool bluetooth accessories that help us out, GPS units, multi-mode phones that also connect to Wi-Fi hotspots. Now taking all this into account, you are virtually connected anywhere and anytime, right? Why would your average CEO not leverage this technology to allow their workers to work from anywhere?
Let's think this scenario all the way through. We have Average Worker X. Let's make it complicated and let's say he's an IT worker. I'm going to use the IT worker example since there aren't that many roadblocks to encounter when your function exists in marketing, sales, accounting, or a few other places. Manufacturing would be an exception to this idea. If you give the worker the tools to connect from anywhere, you might not get all the "face time" that we are all accustomed to, but in turn you have a worker that is more willing to devote time and effort into their workday because they are allowed to have the day to day distractions of chatting with friends, attending other things that are part of their personal life, and the general satisfaction of that if something comes up, they aren't "chained" to their desk. This means you're not working the traditional 9 to 5. You're working 24-7. You have a better ROI on your employees since they are more willing to stay with your company. You have less costs in searching for new talent and you have the tools to retain your top talent. Is this not a win-win for everyone?